More than four fifths of your daily security fixes happen on their own.
Auto Fix takes routine patching and hardening — across Windows and Microsoft 365 — off your team. Only the genuine exceptions get ticketed to a human.
One rule engine, one agent — find and fix live on the same record, all day, every day.
- Patches deployed minutes after release
- Windows & Microsoft 365 hardening enforced
- Every fix proven & logged
- Only what needs human judgment
- Full context, straight to your queue
Fixes that enforce themselves.
Four fifths of your security fixes happen without human touch. Your team moves from patch-queuing to strategy.
What gets in the way
- Weekly patch queues. Hand-queuing patches every week before they reach endpoints.
- Weeks between find and fix. Vulnerabilities sit in a queue until someone logs in to remediate.
- Drift goes undetected. Configuration hardens once, then decays; you cannot prove baselines hold.
- Compliance evidence scattered. Hunting and reassembling fixes across systems before audit season.
How RoboShadow answers it
- Rules enforce hourly. One rule engine runs 24/7; fixes apply without a queue, exceptions surface as tickets.
- Patches deploy in minutes. Minutes after release, not weeks later; exposure window collapses from days to hours.
- Drift caught and fixed automatically. Configuration drift detected in real time; fixes applied, proof attached to the same record.
- Audit-ready from day one. Every fix logged, timestamped, reversible; compliance reports export in seconds, not weeks.
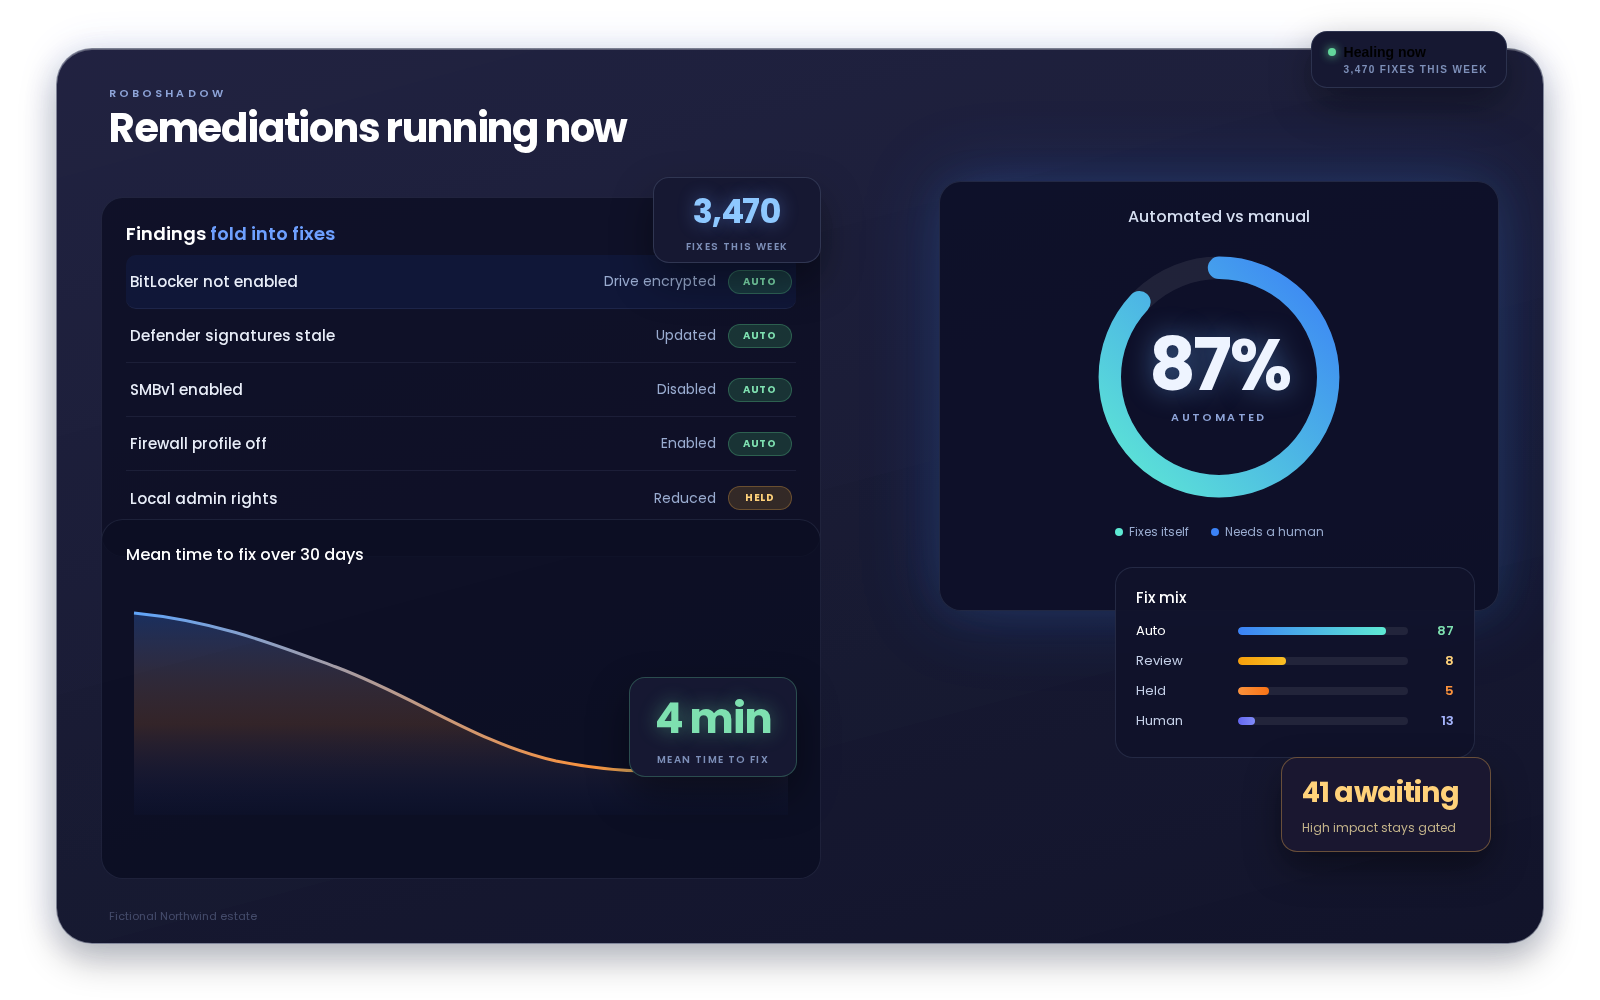
Routine findings fold into fixes on their own. 87% automated. High impact stays gated.
Find, fix, and prove it
Find vulnerabilities and drift
Continuous inventory and patch scanning across all devices in real time.
Automate remediation
Patches and hardening apply within minutes, staged rollout, automatic rollback if needed.
Audit and ticket exceptions
Full compliance trail logged. Non-automatable findings routed to your PSA.
One agent, one rule engine, all your fixes.
Set a policy once. The agent enforces it every hour, every device, every time. No more tool swapping, no more data between systems, no per-module pricing.
Software inventory and patch discovery
Know what's installed on every device and which patches are available before they become disasters. Real-time, continuous, no manual inventory updates.
Automated patch deployment
Deploy patches minutes after release, not weeks later. Test on a pilot group first. Rollback automatically if anything breaks. Your exposure window shrinks from days to hours.
Policy-driven configuration hardening
Enforce CIS, NIST, or your own baselines continuously across the estate. Devices that drift are fixed automatically. No more manual compliance checking or out-of-band hardening work.
PSA ticketing for exceptions
Anything that can't be automated tickets directly into your PSA with full context. Your team sees only what actually needs human judgment, not routine patch queues.
Rollback and compliance proof
Every fix is logged, reversible, and provable. Auditors see the full chain of what changed, when, and why. Incident investigation becomes minutes instead of days.
Flexible scheduling and exclusions
Match your change windows and maintenance schedules. Protect critical systems, VIPs, and production. One policy engine, granular control at device, group, or org level.
See the full feature set in Pricing
This is one of nine tools on a single lightweight agent. See every capability, which tier it sits in, and transparent per-device pricing with no per-module upsell.