The truth about every endpoint.
Patch status, security benchmarks, vulnerabilities and encryption should never live in separate worlds. RoboShadow brings the whole device story together, continuously, on one record.
When device truth is scattered
- Patch and vulnerability data sit across different vendor dashboards.
- Security baselines age quietly in spreadsheets.
- Encryption gaps and configuration drift surface too late.
- Audit evidence becomes a last-minute hunt through tickets and screenshots.
One agent brings it together
- See health, vulnerabilities, patching and controls on one device record.
- Measure every endpoint against the benchmark that matters to you.
- Spot drift and missing encryption as soon as the device reports.
- Keep timestamped evidence ready for customers, teams and auditors.
One agent. Every device. Always checking.
Every machine you run, continuously read and checked against the standards that actually matter — so nothing quietly drifts out of line.
Compliance
One record. All frameworks. Zero spreadsheets.
Your findings and their fixes live on the same platform, auto-mapped to ISO 27001, NIST CSF 2.0, NIST 800-171 and SOC 2 at scan time.
What gets in the way
- Scattered evidence. Findings live in five places, owned by different teams.
- Manual spreadsheet hell. Each framework needs a separate export and weeks of alignment work.
- Proof lags behind fixes. A single vulnerability takes three weeks to move from found to proven fixed.
- Auditors see stale data. Your scanner found it, but your compliance console has not synced it yet.
How RoboShadow answers it
- One timestamp, one truth. Finding, remediation and audit proof all live on the same platform.
- Framework-ready in 60 seconds. Export ISO, NIST and SOC 2 evidence as Word, PDF or spreadsheet, controls mapped to live findings.
- Compliance updates automatically. The moment you remediate, your audit record updates, with no spreadsheet handoffs.
- Drift surfaces in real time. Misconfigurations and missing patches flag as control failures immediately.
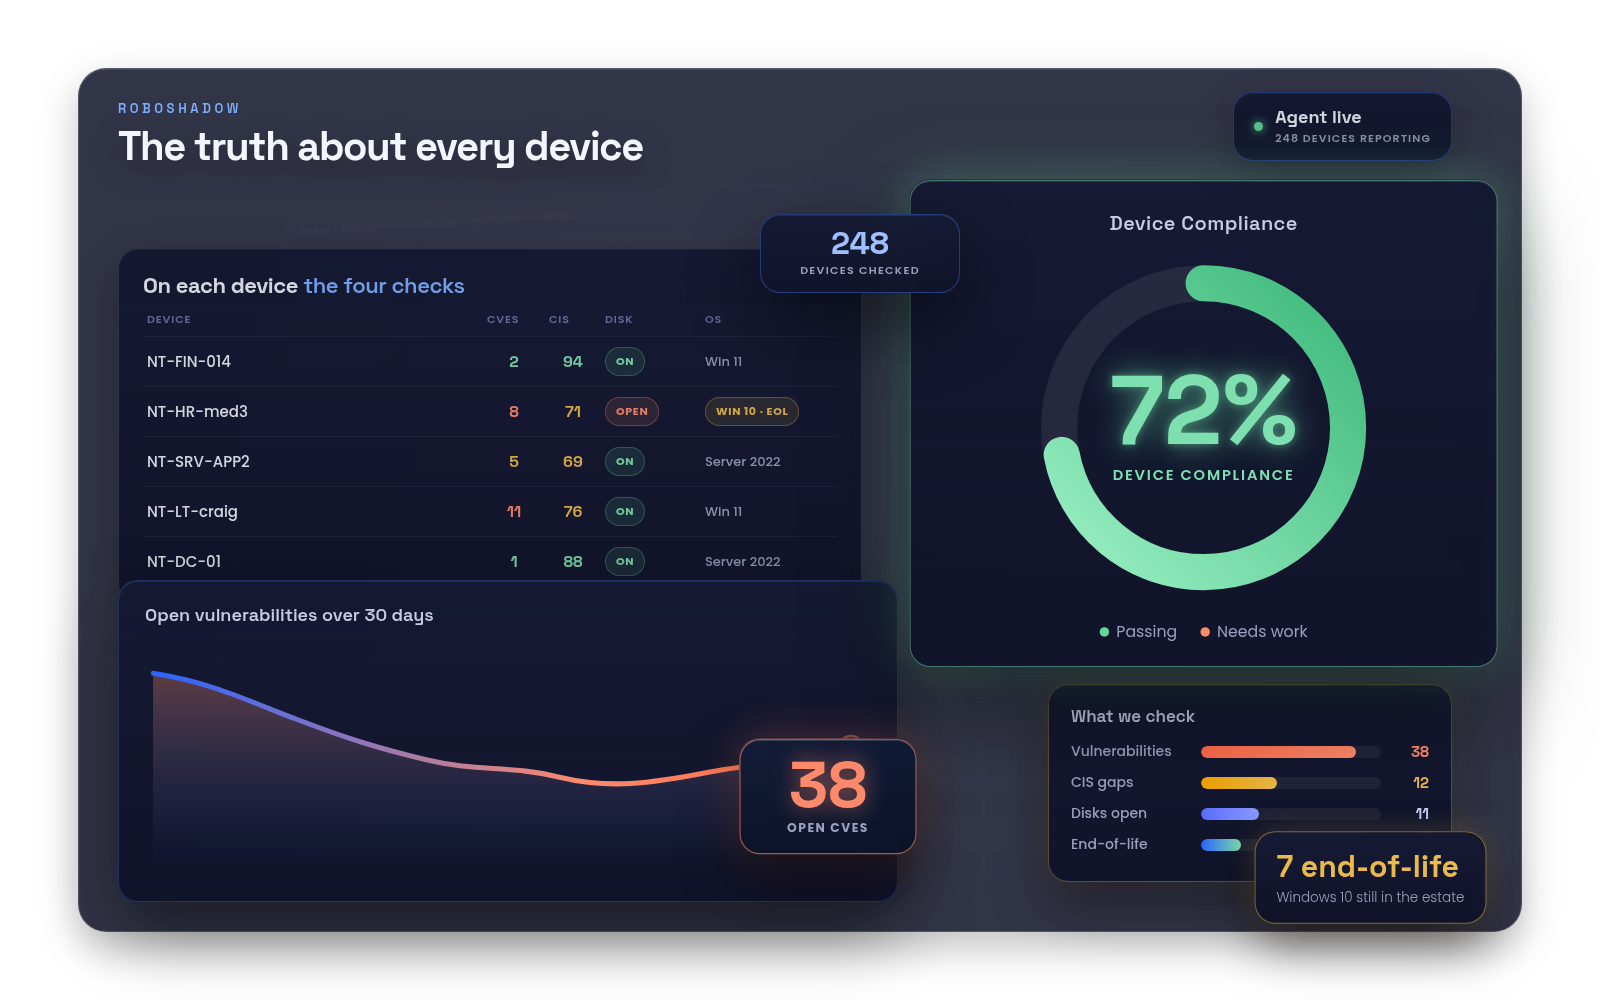
Device Compliance at 72%, with vulnerabilities, CIS benchmarks and end-of-life operating systems on one record per device.
Deploy. Scan. Comply.
Install one agent
Roll out one lightweight agent to every endpoint.
Continuous assessment
Real-time patch status, baselines, drift, and controls.
Audit-ready proof
Timestamped evidence on every device, ready instantly.
Nine capabilities, one device record.
Patch inventory
Missing updates across Windows, Linux, and macOS live in one searchable view, refreshed continuously. See which devices are exposed, prioritise by severity and CVSS score, fix on the same record.
Baseline compliance
Load CIS benchmarks (or build your own hardening template) and measure every endpoint against it continuously. The moment any device drifts, you know which control failed and why, on the same record.
Configuration drift
Detect when any device drifts from your approved state, the moment it happens. Alerts identify exactly which setting changed, when, and why, so you can decide to fix or rollback without delay.
Control inventory
See which required software, settings, and security controls live on each device and which are missing. Missing antivirus, disabled MFA, absent EDR, orphaned accounts all show on the same device view in real time.
Audit evidence
Per-device compliance snapshot with timestamp, signed audit trail, and forensic detail. Export as PDF or spreadsheet for auditors or regulators in seconds, not days.
Compliance reporting
ISO 27001:2022, NIST CSF 2.0, SOC 2, NIST 800-171. One-click framework-aligned reports with per-device proof. No stitching data from five systems. Everything on one platform.
Related RoboShadow products.
Security RMM
Find and fix endpoint misconfigurations at scale, hands-free.
Explore →External Scanner
Find vulnerabilities on your external-facing assets every day.
Explore →AI Auto Fix
Fix findings hands-free and instantly, without manual intervention or waiting for approval.
Explore →Microsoft 365 Compliance
Audit Microsoft 365 tenant settings and user security posture.
Explore →See your endpoints clearly. Start free today.
Deploy one lightweight agent to every device and have the truth about your entire estate in minutes. No card needed.
Device Compliance: The truth about every endpoint.
Know exactly what you have, what is missing, and what is broken. One lightweight agent tracks patch status and configuration across every Windows, Mac, and Linux machine. Your inventory is real, your audit trail is complete.